Purpose
Inspect recorded actions and signature context, and understand what ledger verification can and cannot demonstrate.
Expected outcome
You can filter events, interpret UTC timestamps, identify expected Account-view sequence gaps and escalate integrity failures.
Prerequisites
Audit.View and the appropriate Account scope. Signature execution additionally requires the relevant operational permission and authenticated signer.
Section 1: Search the ledger
- Open Audit Trail.
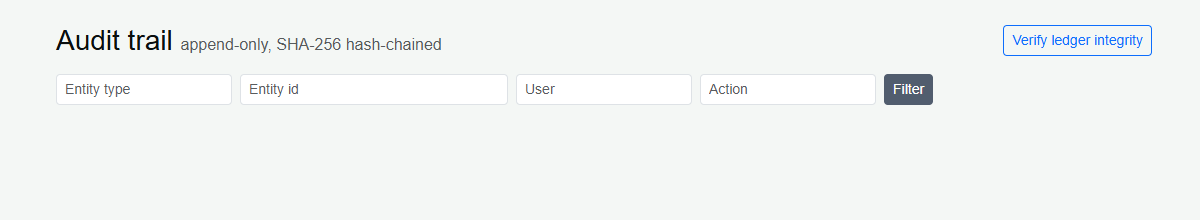
- Enter optional Entity type/ID, User and Action filters.
- Apply Filter; combined criteria narrow results and return the first page.
- Review sequence, UTC timestamp, actor, action, entity, details and recorded hash.
- Use pagination; on narrow screens expand Details where provided.
Account users see events attributed to their own Account. Legacy unattributed events remain System Admin-only.
Section 2: Verify integrity
The verification action checks visible events and predecessor linkage; System Admin can check the complete chain. Account-view sequence gaps can be expected because the chain is shared across Accounts.
A passing result checks recorded integrity relationships. It does not establish completeness, prevent every privileged storage modification, prove encryption, or certify Part 11 compliance. Preserve evidence and escalate a failure; do not manually repair rows or hashes.
Section 3: Signed workflow context
Supported actions such as packaging completion, excursion disposition, lifecycle changes and Account-document operations request authentication and justification. The meaning is linked to the affected operation. Enter an accurate reason; credentials must never be copied into the reason field.
Account isolation and visibility
Audit access does not grant visibility into another Account. Account users see only their Account's attributed events, including permitted account-level activity; filters and exports must not be used to cross organization boundaries. Unattributed legacy or global events remain reserved for System Admin review.
Regulatory context and checks
Assess controls against applicable predicate rules and 21 CFR Part 11, including 11.10(e), 11.50, 11.70 and 11.200, with intended-use validation and organizational procedures. The public website's screenshots are not complete audit-record exports.
This guide supports training and does not authorize clinical decisions, override access controls or establish regulatory compliance. The approved protocol and organizational procedures remain authoritative.